Council documents reveal an ambition to connect personal records from birth registration, housing and social care. A new £10.5 million technology contract and plans for predictive artificial intelligence raise questions about privacy, human rights, democratic oversight and the growing dependence of government on private technology companies. When participating in ordinary civic life is unavoidable, what meaningful control will residents have over the information gathered about them and the conclusions artificial intelligence may draw from it?
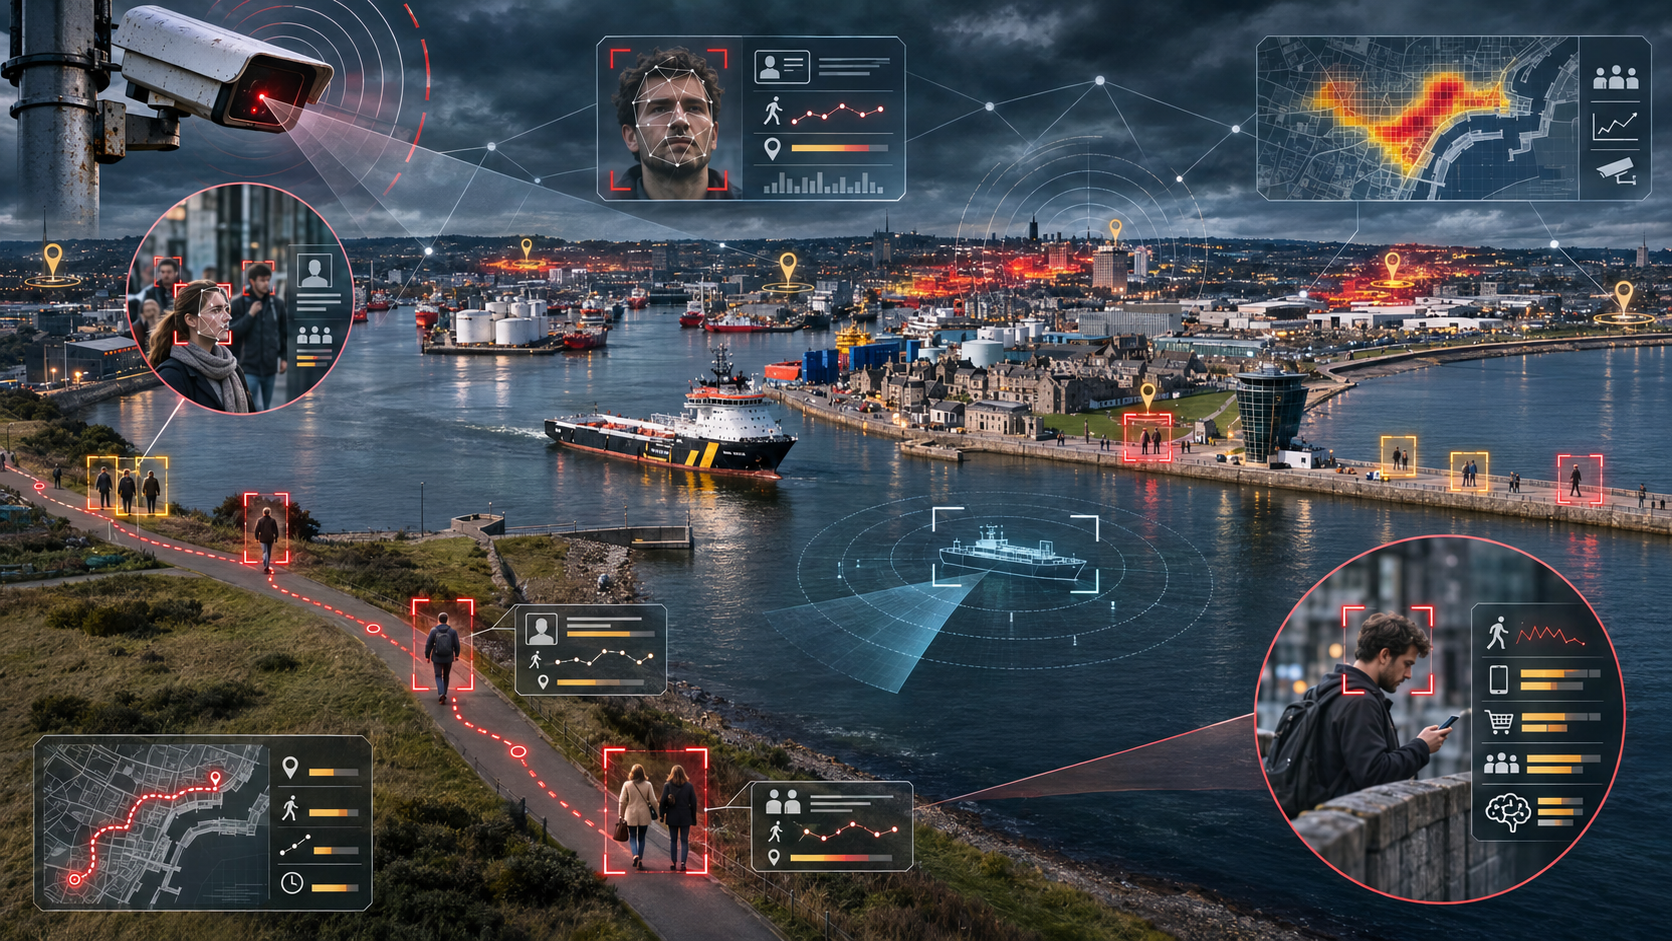
Aberdeen City Council has documented an ambition to create a single digital record for each council customer, connecting information from different public services within Microsoft’s Dynamics 365 technology.
The proposal, disclosed in an internal audit presented to councillors in November 2023, envisages an individual record that could be updated through interactions with the council, including registering a birth, seeking housing assistance and receiving social care.
The document describes the objective as creating a “single, secure record for each Council customer”.
Now Aberdeen is expanding its partnership with Microsoft and Hitachi Solutions through a programme that proposes using artificial intelligence to analyse connected information, identify potential risks concerning individuals and help public services intervene before problems become more serious.
A £10.5 million contract, excluding VAT, was awarded to Hitachi Solutions Europe in March 2026. Its scope includes business and digital strategy development, system design, impact assessments and integration with existing council technology.
The partnership was publicly announced by Hitachi Solutions on 22 September and distributed again on 10 November.
The council says the changes will improve services for approximately 230,000 residents, reduce administration and enable professionals to provide more timely support.
But the combination of connected personal records, predictive analysis and commercially supplied technology raises questions that extend far beyond the immediate benefits of digital government.
Who will decide what information can be combined? Can residents challenge conclusions generated about them? How much practical influence will commercial suppliers acquire over public administration? And what safeguards will prevent information collected for one purpose from being used for another?
Similar systems introduced in the European Union or United States could face additional legal scrutiny, depending on how they operate.
What Would Happen Under EU and American Law?
European and American authorities can legally purchase Microsoft’s technology and develop connected government services. However, particular uses of personal information, predictive AI and surveillance can trigger mandatory assessments, restrictions and public approval procedures.
The following comparison identifies the principal legal issues that an Aberdeen-style programme could encounter. It does not imply that every requirement would automatically apply or that the programme would necessarily be prohibited.
| Jurisdiction and legal concern | Relevant law | What the authorities and suppliers would need to address | Legal timescale or process |
|---|---|---|---|
| EU: Linking personal records across government services | General Data Protection Regulation (GDPR), Articles 5, 6, 9 and 35 | Establish lawful purposes for data-sharing, justify processing sensitive information, restrict access and complete a Data Protection Impact Assessment (DPIA) where high-risk processing is proposed. | Assessment before relevant processing begins. No fixed statutory completion period. |
| EU: High-risk processing requiring consultation | GDPR, Article 36 | If a DPIA identifies risks that cannot be sufficiently mitigated, the authority must consult the data-protection regulator before processing. | Regulator’s advice period: up to 8 weeks, extendable by 6 weeks. Requests for further information can suspend the clock. |
| EU: AI evaluating eligibility for essential public assistance | EU Artificial Intelligence Act, Annex III, Articles 27 and 49 | Qualifying high-risk AI systems face requirements including fundamental-rights assessments, human oversight and registration obligations. | Principal Annex III high-risk requirements apply from 2 December 2027. Applicable checks must precede deployment; no fixed assessment duration. |
| EU: AI-generated social scoring | EU Artificial Intelligence Act, Article 5 | Specified forms of AI social scoring that lead to prohibited detrimental treatment are unlawful. A connected personal record alone does not constitute prohibited social scoring. | Prohibition already applies. A prohibited system must be redesigned or abandoned; there is no approval period. |
| EU: Significant decisions made solely by AI | GDPR, Article 22 | A lawful exception and appropriate safeguards are needed for solely automated decisions producing legal or similarly significant effects. | Requirements must be satisfied before use. No fixed approval timetable. |
| USA: Sharing children’s education records | Family Educational Rights and Privacy Act (FERPA), 20 USC §1232g; 34 CFR Part 99 | Covered educational records cannot simply be transferred to commercial systems for unrestricted reuse. Contractors must satisfy applicable disclosure conditions, including institutional control and purpose restrictions. | Compliance arrangements before disclosure. No nationwide approval period. |
| USA: Processing protected healthcare information | Health Insurance Portability and Accountability Act (HIPAA) | Where covered healthcare information is involved, relevant cloud providers and contractors must meet security and business-associate requirements. | Required agreements and safeguards before processing. No fixed statutory review period. |
| USA: Automated decisions affecting welfare benefits | Fourteenth Amendment; Goldberg v. Kelly (1970) | Government must preserve applicable due-process protections, including notice and hearing rights in covered circumstances. Automated assessments cannot remove those protections. | Required procedures before covered adverse decisions; no fixed project approval timetable. |
| USA: Qualifying municipal surveillance technology | San Francisco Administrative Code, Chapter 19B | Certain surveillance systems require an impact report, a publicly reviewed technology policy and approval by the Board of Supervisors, subject to exceptions. | Impact report and proposed policy published at least 30 days before the first relevant public meeting. Additional approval time is not fixed. |
Legal position as at 10 November 2026. The American requirements vary according to state, municipality and the information involved. The EU AI Act’s principal high-risk rules for Annex III systems are not yet applicable, although GDPR protections and specified AI prohibitions already apply.
Scotland Has Protections Too, but the Rules Differ
Aberdeen is outside the European Union, and the EU Artificial Intelligence Act does not generally apply to its domestic council activities.
The United Kingdom has not introduced an equivalent comprehensive law classifying particular uses of AI in public assistance as high-risk.
The Data (Use and Access) Act 2025 also expanded the circumstances in which organisations can make significant decisions based solely on automated processing, with relevant provisions taking effect in February 2026.
Such decisions remain subject to safeguards, including opportunities for individuals to receive information, challenge decisions and obtain human intervention.
Scotland is not without legal protections. The UK GDPR, Data Protection Act 2018 and Human Rights Act 1998 apply to Aberdeen City Council. High-risk processing can require an impact assessment, and where unmitigated high risks remain, prior consultation with the Information Commissioner’s Office is necessary.
The ICO’s normal advice period is eight weeks, extendable to fourteen weeks in complex cases. The regulator can also take action to prevent unlawful processing.
The difference is therefore not that Aberdeen operates without data-protection legislation. It is that the EU imposes additional AI-specific obligations for certain public-sector applications, while American law provides a combination of constitutional protections, federal sector-specific requirements and state or municipal controls.
Whether Aberdeen has completed equivalent scrutiny for its proposed cross-service record and predictive AI uses is a question that requires examination of the council’s actual assessments, contracts and technical arrangements.
The Plan for a Record That Could Begin at Birth
The most revealing description of Aberdeen’s ambitions was not contained in the latest corporate announcement.
It appeared in the council’s own Care Management System internal audit, dated 17 October 2023 and presented to the Audit, Risk and Scrutiny Committee the following month.
The report examined Microsoft Dynamics 365 for Social Work, developed in partnership with Microsoft and Hitachi from 2020 and introduced in October 2022.
Initially, the platform replaced the previous CareFirst system, bringing relevant social care records, assessments, payments and workflows together.
The audit explained that Dynamics 365 was also being developed to support predictive artificial intelligence and that its wider ambition involved a single record for each council customer.
It specifically referred to birth registration, housing support and social care as examples of interactions that could update the same record.
The proposal also contemplated improved sharing arrangements involving housing officers and relevant partners, including Bon Accord Care and the NHS.
This is considerably more significant than introducing an online form or replacing an outdated computer system.
Birth registration establishes fundamental information about a person. Housing applications may contain details of income, employment, household relationships and personal difficulties. Social work files can contain sensitive assessments of health, disability, family circumstances or risks involving children.
Each category of information is collected for a particular purpose.
Connecting them does not necessarily mean every employee can access everything. Aberdeen’s stated intention is to give appropriately authorised staff access to relevant information.
Nevertheless, the ability to connect records creates new possibilities for analysing an individual’s history across services.
A record that begins with one legitimate administrative transaction could potentially become part of a much broader history of interactions with local government.
It is important to distinguish the ambition from its implementation. The 2023 audit does not prove that a comprehensive file has already been created for every Aberdeen resident, or that every council department now contributes information to it.
Nor does it demonstrate unrestricted access by Microsoft, Hitachi or government employees.
It does, however, establish that the council has expressly contemplated a connected personal record extending beyond a single department.
The extent to which this vision has already been implemented has not been established from the documents examined for this article.
Why Predictive Artificial Intelligence Changes the Question
A database stores information. Predictive artificial intelligence can use information to identify patterns and generate assessments about people.
That difference is central to Aberdeen’s new programme.
The September announcement describes plans to bring together data from multiple sources in a unified model and use advanced analytics and AI to identify potential risk indicators earlier.
The proposed objective is preventative assistance.
A social worker might be alerted to circumstances suggesting that somebody needs additional support. Professionals might identify growing difficulties in a household before an emergency develops.
Better coordination could reduce the need for residents to repeat distressing information to multiple departments. It could also help prevent people from being overlooked.
Those are legitimate public-service objectives.
But when an automated system begins interpreting personal information, new risks arise.
Information entered by an employee may be incomplete or inaccurate. Events may be recorded without sufficient context. Patterns that appear statistically significant may not accurately describe an individual.
A system may consequently produce an assessment that is incorrect, misleading or unnecessarily intrusive.
The effects could be amplified if the assessment becomes part of a shared record and influences later interactions with other services.
Consider an individual who receives an inaccurate risk classification. Even if the original assessment was intended to be helpful, subsequent practitioners might encounter that classification before meeting the person concerned.
Their judgement could be influenced by information the individual does not know exists and has not had an opportunity to challenge.
This is a foreseeable risk of connected predictive systems, not evidence that Aberdeen is already making such classifications.
The announcement does not establish that Microsoft or Hitachi will independently determine who receives social care, housing assistance or other statutory services.
The council says AI will support practitioners in making decisions.
The important question is whether that human oversight will be sufficiently informed, independent and effective to identify mistakes rather than simply approving computer-generated recommendations.
The more influential automated assessments become, the more consequential that distinction becomes.
Aberdeen’s Own Audit Had Already Raised Data-Access Concerns
The 2023 internal audit identified a specific issue involving third-party access to sensitive information.
At the time of the review, the support and maintenance supplier had access to special-category personal data held within the live Dynamics 365 environment.
Auditors questioned whether that access needed to remain available outside periods when the supplier was undertaking relevant system development.
They warned that insufficient restrictions could breach the UK GDPR data-minimisation principle and expose the council to regulatory action and financial or reputational harm.
The audit also recorded feedback suggesting that some internal teams could access records beyond what their immediate responsibilities required.
Council management explained that access arrangements were intended to support coordinated work across different social work services.
The report recommended reviewing third-party restrictions, and management agreed to improvements.
The overall assessment was substantial assurance. The auditors identified no severe or major risks and did not conclude that personal information had been misused.
The findings date from 2023 and cannot establish whether the same access issues remain unresolved today.
There is also evidence that privacy assessments have been undertaken for parts of Aberdeen’s digital programme. The 2023 audit referred to an existing assessment documenting access decisions, while a September 2025 Integration Joint Board paper stated that a full Data Protection Impact Assessment had been completed for its electronic medication-administration project.
It would therefore be incorrect to suggest that Aberdeen has undertaken no data-protection assessments.
What remains to be established is whether assessments covering the proposed unified record and predictive AI uses have been completed, what risks they identified and how those risks have been addressed.
Microsoft Has Been Involved for Seven Years
Aberdeen’s relationship with Microsoft predates the current artificial intelligence programme.
On 13 August 2019, Microsoft announced that Aberdeen City Council had become the first Scottish local authority to use its Cloud Navigator digital transformation programme.
The initiative involved migration towards Microsoft’s Azure cloud infrastructure and the introduction of new digital services.
Microsoft described the arrangement as an opportunity to improve efficiency, strengthen security and enable more advanced uses of data.
The relationship subsequently expanded into social work systems and other council operations.
The original partnership began while the United Kingdom was still a member of the European Union. It therefore cannot reasonably be described as having begun to evade the EU Artificial Intelligence Act, which did not yet exist.
The changing regulatory environment may still be relevant to the scope of later AI developments, but there is no established evidence that Microsoft or Hitachi selected Aberdeen in order to avoid European or American law.
A more immediate explanation is the council’s existing dependence on Microsoft technology and its continuing investment in systems built around that environment.
Hitachi Solutions describes itself as dedicated exclusively to the Microsoft ecosystem.
That specialisation can give the council access to experienced developers familiar with its existing systems. It also raises questions about how competing technologies are evaluated and whether future services can be transferred to other suppliers.
The companies are not simply selling isolated products. The March 2026 contract includes strategic advice, design and integration, activities that can influence how public services operate.
The concern is not that a private company possesses technological expertise.
It is whether public authorities retain sufficient independence to question that expertise, reject proposals, change suppliers and determine how public powers are exercised.
The £10.5 Million Contract
Public Contracts Scotland records show that Aberdeen City Council awarded Hitachi Solutions Europe a contract worth £10.5 million, excluding VAT, on 23 March 2026.
The contract covers consultancy and implementation of Microsoft business applications and data services.
Its published scope includes strategy development, requirements definition, technical architecture, impact assessments, configuration, customisation and integration with existing systems.
The notice records one tender and identifies the Crown Commercial Service’s G-Cloud 14 framework as the procurement route.
A single recorded tender is not evidence of wrongdoing. Framework procurement can lawfully operate through established purchasing arrangements without a fresh open competition for every award.
However, the size and strategic significance of the contract make the selection process, assessment of alternatives and long-term costs matters of legitimate public interest.
Two additional contracts awarded to Hitachi in 2025 concerned a Microsoft Dynamics 365 human resources implementation, valued at approximately £1.58 million, and technology-enabled care solutions, valued at £1.2 million.
These are published contract values, not verified expenditure already incurred. The relationship between separate awards and existing transformation budgets also needs clarification.
The longer-term financial issue is the cost of dependency.
When a council relies on one commercial technology environment for an increasing range of essential services, replacing it may involve more than purchasing alternative software.
Records may need to be transferred, applications rebuilt, integrations replaced and thousands of employees retrained.
A future administration may consequently face practical and financial barriers to changing the systems inherited from its predecessors.
That is why ownership of data, contractual exit provisions, technical interoperability and independent auditing matter as much as the initial procurement price.
A European Court Has Already Rejected a Government Data-Profiling System
One important precedent comes from the Netherlands.
In February 2020, the District Court of The Hague ruled that legislation governing the Dutch government’s System Risk Indication programme, known as SyRI, breached Article 8 of the European Convention on Human Rights.
The programme was intended to analyse information from different public sources to detect potential welfare and tax fraud.
The court concluded that the arrangements failed to strike a fair balance between the government’s objectives and individuals’ rights to privacy.
Insufficient transparency and the difficulty of verifying how the system operated were central concerns.
Aberdeen’s stated objectives are different. Its proposals emphasise identifying people who may need assistance, rather than investigating suspected fraud.
The Dutch ruling does not establish that Aberdeen’s programme is unlawful.
It does demonstrate that the use of connected government information for automated risk identification can engage fundamental rights, even when a public authority believes the programme serves an important public purpose.
Article 8 remains relevant to Scotland through the Human Rights Act.
The right to privacy is not absolute, but interference must have a lawful basis and satisfy the applicable necessity and proportionality requirements.
A technology’s ability to identify patterns more efficiently does not, by itself, establish that government is entitled to collect or analyse every category of information that might improve a prediction.
America Provides Another Warning
The United States has experienced serious failures involving automated public administration.
Between 2013 and 2015, Michigan’s automated unemployment insurance system, known as MiDAS, falsely accused thousands of people of benefit fraud.
A subsequent class action alleged that the system had made fraud determinations without adequate human oversight and that people had suffered financial losses without due process.
Michigan’s Attorney General announced a $20 million settlement in October 2022.
The case concerned an American state government, not Microsoft or Aberdeen City Council.
It illustrates how automated administrative systems can cause substantial harm when errors become the basis for consequential government action.
The US Constitution provides procedural protections that cannot simply be removed by introducing software.
In Goldberg v. Kelly in 1970, the US Supreme Court established significant due-process protections before the termination of covered welfare benefits.
Other American laws regulate particular categories of information, including school educational records and protected healthcare information.
Some municipalities impose additional requirements. San Francisco’s surveillance-technology ordinance requires public review and legislative approval for qualifying systems, subject to specified exceptions.
These protections do not amount to a nationwide prohibition on connected government databases or AI-assisted services.
They demonstrate that the legal questions depend on what a system actually does, what information it uses and what consequences it can produce.
Were Aberdeen Residents Asked?
Aberdeen has undertaken public engagement concerning digital services.
Aberdeen City Health and Social Care Partnership advertised co-production sessions in August and September 2026, inviting residents, community organisations and service providers to discuss digital health and social care.
The invitations acknowledged concerns about accessibility, confidence, skills and access to technology.
Such engagement is relevant and should not be overlooked.
But the £10.5 million Hitachi contract had already been awarded in March.
The public documents examined for this article do not establish that residents were specifically asked whether they supported a connected administrative record encompassing multiple stages of life, or what limits they wanted placed on predictive analysis of their information.
Nor have they established that residents were presented with alternative technical approaches before the council made its principal contractual commitments.
This is not proof that consultation was absent or legally deficient.
Local authorities can make procurement decisions through elected representatives and authorised officials without holding a public vote on each contract.
Nevertheless, consultation about the convenience of digital services is not necessarily the same as consultation about the architecture through which residents’ personal information may be collected and analysed.
A person may support improved coordination between social workers and healthcare professionals while opposing the creation of a broad personal record accessible across multiple government functions.
Someone may welcome AI-generated meeting notes but object to automated risk assessments becoming part of their administrative history.
Meaningful public engagement depends partly on whether those different choices are explained and whether participants have an opportunity to influence them.
The council should be able to establish what residents were told, how many participated, what concerns were expressed and what changes followed.
Where Government Ends and Private Technology Begins
The relationship between public institutions and commercial technology companies is not new.
Councils have long purchased software, maintained databases and employed outside specialists.
The difference emerging with advanced AI is the range of functions that commercial systems may perform.
A company can provide the infrastructure that stores information, the software that connects records, the tools that analyse them and the systems through which officials encounter the resulting assessments.
None of those activities automatically transfers statutory authority to the supplier.
But technical systems can shape the practical exercise of authority.
They influence what information is available, how it is organised, which connections are identified and which possible actions are brought to an official’s attention.
The resulting influence may be difficult to measure because it is embedded in routine administrative processes rather than expressed through formal policy decisions.
A council could remain legally responsible for its services while becoming increasingly dependent on technology it cannot independently reproduce, fully examine or readily replace.
That is a risk to institutional independence, not proof that Aberdeen has already surrendered control.
The published partnership statement refers to future smart-city opportunities. It does not establish that the city has introduced comprehensive surveillance, compulsory digital identification or unrestricted automated monitoring.
It also does not demonstrate that Microsoft or Hitachi is using residents’ information to train general-purpose AI models.
Such claims would require evidence concerning the actual systems, contracts and data-processing arrangements.
The documented issue is already substantial without assuming those developments have occurred.
Aberdeen has described an ambition to connect individual records across services. It has introduced Microsoft-based social work systems. It is expanding predictive AI capabilities. And it has awarded substantial contracts to a company specialising in the same technology environment.
The question is what limits have been established before these capabilities are extended further.
The Rights of Future Generations
A digital record created for a legitimate purpose today may outlive the officials, councillors and governments responsible for introducing it.
Future administrations may inherit systems that contain years of interconnected personal information.
Technology may also develop in ways that make it possible to extract conclusions from older records that could not have been anticipated when those records were collected.
This raises questions about retention, future access, new uses of information and the ability of individuals to correct or challenge records created years earlier.
Historically, different public departments have often maintained separate records for separate administrative functions. Those arrangements did not guarantee privacy, but they could impose practical and institutional limits on combining information.
Connected digital systems can remove those barriers.
The same technological capabilities that allow government to coordinate assistance can also make extensive profiling easier if legal, technical and organisational controls are inadequate.
Artificial intelligence increases the importance of these controls because it can transform recorded events into interpretations and predictions.
That distinction matters particularly for children.
Information recorded about a child or family may reflect temporary circumstances, professional judgements or events that should not define the individual indefinitely.
Safeguards must therefore address not only unauthorised access but also accuracy, context, retention and the potential consequences of reusing information over time.
The United Nations Convention on the Rights of the Child recognises protections concerning children’s privacy and their interests in decisions affecting them. Scotland’s 2024 incorporation legislation gives specified Convention requirements domestic legal effect within its defined scope.
The long-term question is whether systems developed for present administrative convenience preserve those protections as their capabilities expand.
What Aberdeen Must Be Able to Explain
Several essential questions remain unanswered by the published announcement and the records examined for this article.
The first concerns the individual record itself.
Does the ambition described in the 2023 audit remain part of Aberdeen’s approved digital strategy? Which services currently contribute information to a common customer record, and which additional connections are planned?
The council should identify the information categories involved, the lawful purposes for linking them, the retention arrangements and the circumstances in which other departments or partner organisations may obtain access.
The second concerns artificial intelligence.
Which specific AI systems are operational, which remain under development and what types of information are they permitted to analyse? Will they produce individual risk indicators, and can those indicators materially influence decisions about care, safeguarding, housing or other services?
If an assessment is incorrect, how can the person concerned discover it and seek correction?
The third concerns the commercial relationship.
What technical access do Microsoft, Hitachi and their subcontractors possess? Are contractors permitted to use information for system development or model improvement? Can Aberdeen independently audit the software, inspect relevant processing and transfer essential services to another provider?
The fourth concerns democratic oversight.
Which elected body or delegated official authorised the latest contract and associated processing arrangements? What public consultation took place specifically on the proposed single-record model and predictive AI? Were alternative approaches considered?
Finally, what evidence demonstrates that the recommendations made in the 2023 internal audit were implemented?
These questions do not presume wrongdoing.
They concern the evidence necessary to establish whether a public authority has retained effective control over systems that may increasingly influence its relationship with residents.
The relevant contracts, completed privacy and human-rights assessments, consultation findings and audit follow-up records would allow a more definitive examination than the companies’ announcement provides.
A Decision Bigger Than Software
Aberdeen’s programme could improve the delivery of important services.
Better information-sharing may prevent vulnerable people from being overlooked. Reduced administration may allow social workers to spend more time with families. Modern technology may help a council manage growing pressures on public resources.
Those possibilities deserve consideration.
So do the consequences of making increasingly connected personal information and commercial AI systems central to public administration.
A system can be efficient without being sufficiently accountable. Information can be securely stored yet used for purposes that require separate justification. A human official can retain formal responsibility while becoming heavily dependent on automated assessments.
The ambition to create a single digital record for each council customer brings these questions into focus because it establishes the possibility of information following a person across different interactions with local government.
Predictive artificial intelligence then adds the possibility of generating conclusions from that information.
The resulting infrastructure could have consequences extending far beyond the current council administration or the duration of the commercial contracts.
Microsoft and Hitachi have not been shown to possess Aberdeen’s statutory governing powers. Nor has the available evidence established that the proposed programme constitutes unlawful surveillance.
But the council’s own documents establish an ambition to develop more extensively connected personal records, while the latest partnership proposes new ways to analyse the information they contain.
The public-interest issue is therefore not confined to whether the software improves services in the short term.
It concerns whether residents can understand, scrutinise and challenge the systems that may increasingly influence how they are treated by government.
It also concerns whether elected authorities retain sufficient practical independence to control, audit and replace those systems as technology and public expectations change.
The answers will determine whether Aberdeen’s Digital Council of the Future develops with enforceable limits on public and commercial power, and whether those limits remain effective for the generations who inherit it.
Sources
Internal Audit Report AC2405 — Care Management System. Aberdeen City Council, Audit, Risk and Scrutiny Committee, 23 November 2023.
https://committees.aberdeencity.gov.uk/mgConvert2PDF.aspx?ID=151280
Aberdeen City Council, Hitachi Solutions and Microsoft to Build the Digital Council of the Future. Hitachi Solutions, 22 September 2026.
https://global.hitachi-solutions.com/gb/blog/aberdeen-city-council-hitachi-solutions-and-microsoft-to-build-the-digital-council-of-the-future/
Aberdeen City Council, Hitachi Solutions and Microsoft to Build the Digital Council of the Future. PR Newswire, 10 November 2026.
https://www.prnewswire.co.uk/news-releases/aberdeen-city-council-hitachi-solutions-and-microsoft-to-build-the-digital-council-of-the-future-302933833.html
Consultancy and Implementation of Microsoft Business Applications and Data Services. Aberdeen City Council, Public Contracts Scotland, 25 March 2026.
https://www.publiccontractsscotland.gov.uk/search/show/search_view.aspx?ID=MAR552472
Award of Dynamics 365 HR Implementation. Aberdeen City Council, Public Contracts Scotland, 15 July 2025.
https://www.publiccontractsscotland.gov.uk/search/show/search_view.aspx?ID=JUL534756
Microsoft Solutions for Technology Enabled Care 1.0. Aberdeen City Council, Public Contracts Scotland, 29 August 2025.
https://www.publiccontractsscotland.gov.uk/search/show/search_view.aspx?ID=AUG538086
Scottish First for Aberdeen City Council as Digital Transformation Gathers Pace. Microsoft UK Stories, 13 August 2019.
https://ukstories.microsoft.com/features/scottish-first-for-aberdeen-city-council-as-digital-transformation-gathers-pace/
Digital Innovation — Integration Joint Board Public Reports Pack. Aberdeen City Health and Social Care Partnership, 30 September 2025.
https://committees.aberdeencity.gov.uk/documents/g9713/Public%2Breports%2Bpack%2B30th-Sep-2025%2B10.00%2BIntegration%2BJoint%2BBoard.pdf?T=10
Help Shape Aberdeen City’s Digital Strategy. Aberdeen City Health and Social Care Partnership, public engagement announcement, 2026.
https://www.linkedin.com/posts/aberdeen-city-health-and-social-care-partnership_help-shape-aberdeen-citys-digital-strategy-activity-7494652928926978048-WgFI
General Data Protection Regulation, Regulation (EU) 2016/679. European Parliament and Council, 27 April 2016.
https://eur-lex.europa.eu/eli/reg/2016/679/oj/eng
Artificial Intelligence Act, Regulation (EU) 2024/1689, Consolidated Text. European Union, 27 July 2026.
https://eur-lex.europa.eu/eli/reg/2024/1689/2026-07-27/eng
Artificial Intelligence Act: Implementation and Timetable. European Commission, 2026.
https://digital-strategy.ec.europa.eu/en/policies/regulatory-framework-ai
Do We Need to Consult the ICO? Information Commissioner’s Office, UK GDPR guidance.
https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/accountability-and-governance/data-protection-impact-assessments-dpias/do-we-need-to-consult-the-ico/
Data (Use and Access) Act 2025: Data Protection Changes. Information Commissioner’s Office, 2026.
https://ico.org.uk/about-the-ico/what-we-do/legislation-we-cover/data-use-and-access-act-2025/the-data-use-and-access-act-2025-duaa-summary-of-the-changes/data-protection/
Human Rights Act 1998, Section 6. UK Parliament, legislation in force.
https://www.legislation.gov.uk/ukpga/1998/42/section/6
SyRI Legislation in Breach of European Convention on Human Rights. District Court of The Hague, Netherlands Judiciary, 13 February 2020.
https://www.rechtspraak.nl/organisatie-en-contact/organisatie/rechtbanken/rechtbank-den-haag/nieuws/2020/02/syri-legislation-in-breach-of-european-convention-on-human-rights
State of Michigan Announces Settlement of Civil Rights Class Action Alleging False Accusations of Unemployment Fraud. Michigan Attorney General, 20 October 2022.
https://content.govdelivery.com/accounts/MIAG/bulletins/3335987
Goldberg v. Kelly, 397 US 254. Supreme Court of the United States, 23 March 1970.
https://www.law.cornell.edu/supremecourt/text/397/254
Who Is a School Official Under FERPA? US Department of Education, Student Privacy Policy Office.
https://studentprivacy.ed.gov/faq/who-school-official-under-ferpa
Guidance on HIPAA and Cloud Computing. US Department of Health and Human Services.
https://www.hhs.gov/hipaa/for-professionals/special-topics/health-information-technology/cloud-computing/index.html
Acquisition of Surveillance Technology, Chapter 19B. City and County of San Francisco, Administrative Code, Sections 19B.2–19B.4.
https://codelibrary.amlegal.com/codes/san_francisco/latest/sf_admin/0-0-0-61746